

Imagine you receive an email without a single typo. It addresses you by your name, refers to a project from your team, and arrives exactly at the moment when you are actually waiting for a reply. Exactly these kinds of messages are being created with AI today. The same tools that help you in everyday life are also used by attackers, only without terms of use and without ethical brakes. In this guide, I show you where the offensive side stands today and what consequences you should draw from it for your own defense. The goal is not panic, but good preparation.
The video is only loaded from YouTube when you play it – data (including your IP address) is then transmitted to YouTube/Google. More in the privacy policy
Key Takeaways
- Attackers use AI without restrictions: customized models, their own infrastructure, or uncensored open-source models.
- Phishing is linguistically almost flawless and highly personalized. Language errors are therefore no longer useful as a detection feature.
- With just a few seconds of audio material, voices can be cloned, and video deepfakes are becoming more and more convincing in real time.
- Reconnaissance that used to take days now runs in minutes. The barrier to malware development is falling.
- The strongest defense is clear processes and verification via a second channel, not technology or gut feeling alone.
Step 1: Understanding the Attackers' Rules of the Game
Commercial AI services have protective mechanisms that are meant, for example, to prevent the direct creation of malicious code. Attackers operate outside these guardrails. They fall back on modified models, their own infrastructures, or open-source models without filters. What you have learned in this course about log analysis, phishing detection, and scripting, attackers can learn as well, and they are already doing so. Their advantage lies less in new magic than in speed and the absence of inhibitions.

Step 2: Phishing Without Visible Errors
In the past, you could often recognize phishing emails by poor grammar, spelling mistakes, generic greetings like "Dear Customer", fake sender addresses, and unprofessional layout. These features are no longer a reliable yardstick. AI writes naturally in any language, uses idiomatic expressions, and hits the right tone. A sentence like "As part of our regular security review, we have detected unusual activity in your account" seems completely legitimate at first glance. Anyone who only pays attention to language errors relies on an indicator that no longer holds up.

Step 3: Personalization on a Large Scale
AI analyzes LinkedIn profiles, social media activity, and company websites. On this basis, it generates personalized emails for thousands of targets at the same time. The messages refer to real colleagues, ongoing projects, or upcoming events. As a result, each email appears to be an individual message and not a mass mailing. Your takeaway is therefore: Pay attention not only to the content of a request, but to its context. Ask yourself whether the occasion fits your usual daily work and whether you would expect anything from this person or department at all.

Step 4: Pretext and Timing, Using a CFO as an Example
A pretext is a credible story with which an attacker justifies their request. An example from the video: The AI finds out that a company has recently announced an acquisition. It then creates a fake email in the name of the executive management that contains an appropriately named document. This is a perfect pretext with perfect timing. Especially with topics such as acquisitions, financial transactions, or personnel decisions, you should therefore consciously take a pause before you act.

Step 5: Automated Social Engineering Campaigns
Attackers now automate entire campaigns in multiple phases. First, the AI researches targets, especially so-called high value targets such as administrators, employees from the finance department, and executives. Then it creates individual messages for each target and, if necessary, imitates the writing style of known contacts. Contact is made via multiple channels, for example by email as the initial contact, by message with a link as a follow-up, and by a fake call for confirmation. In the last phase, the AI answers follow-up questions appropriately, keeps the conversation going, and builds trust before the actual malicious function comes into play. What used to cost hours of manual work per target now runs fully automated.

Step 6: Cloning Voices and Videos
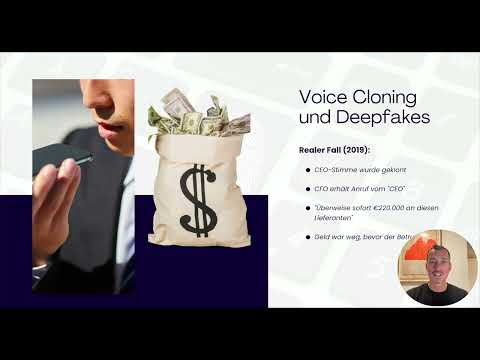
According to the video, around 30 seconds of audio material is enough to convincingly replicate a voice. The sources are often publicly accessible, such as interviews, podcasts, or recordings of company presentations. A documented case from 2019 shows the impact: The cloned voice of a CEO called the finance director and demanded an immediate transfer of 220,000 to a supplier. The money was gone before the fraud was noticed. Real-time video deepfakes are now also possible. An attacker can look like the boss in a video call even though he is not. The quality is not always perfect, but with a poor webcam resolution it is often good enough. Services like HeyGen show how far the technology has already advanced.

Step 7: Business Email Compromise 2.0
Classic fraudulent emails in the name of senior management have existed for a long time. What is new is the combination: The fake email is followed by a fake call for confirmation. This is so-called multifactor social engineering. The defense of many companies relies on trust in familiar voices and faces, and exactly this trust can now be attacked in a targeted way. Your most important takeaway: A confirmation that runs through the same attack channel is not a confirmation. What matters is an independent second channel.

Step 8: Accelerated Malware Development
AI can generate functional code for specific tasks, adapt to different environments, and create variants at high speed. As a result, the expertise required for sophisticated malware decreases, and more actors can develop it. Commercial services prevent the direct generation of malicious code, which is why attackers switch to other models. The hurdle exists, but it is not insurmountable. For you as a defender, this means: Purely signature-based detection no longer meets the requirements, because variants multiply quickly.

Step 9: Automated Reconnaissance and OSINT
Before an attack begins, attackers gather information about the target. AI now handles much of this reconnaissance. It analyzes DNS records and subdomains, correlates data with Shodan-style search engines, and identifies usable components. An organizational chart is created from profiles on business networks and social media platforms, and new employees stand out immediately. The technology stack in use can be derived from job postings. In addition, the AI compares email addresses with known data leaks and creates likely password variants. What used to take days is now done in minutes or seconds. A clear recommendation follows from this: Use a separate password for every service and enable multi-factor authentication.

Step 10: Defense Begins with Processes
Technical protective measures such as SPF, DKIM, and DMARC are becoming more important because they make sender spoofing more difficult. However, they are not sufficient on their own. When it comes to awareness, you must let go of the idea that spelling mistakes are a warning sign. Instead, rely on fixed processes. A money transfer should never take place without confirmation through a second channel. Verify critical requests using an out-of-band procedure by calling a number you already know rather than the number from the suspicious call. Code words for critical transactions and a callback procedure also help. In video calls, you can ask for a small movement task, such as raising a hand. And always maintain a healthy distrust of unusual requests.

Step 11: Defending Against AI-Powered Malware
Behavior-based detection methods that evaluate activities and do not just compare signatures help against AI-generated malware. Modern EDR solutions with machine learning can detect deviations in behavior. Zero-trust approaches verify even known processes instead of automatically trusting them. In addition, fast patching and consistent vulnerability management are indispensable. Also use AI defensively, for example for analysis, correlation, and detection engineering. Finally, regularly practice incident response so that in an emergency you do not first have to figure out what to do.

Summary ??? Understanding AI as an Attack Tool: What Attackers Achieve and How You Protect Yourself
Attackers use AI to scale and personalize phishing, fake voices and videos, develop malware faster, and automate reconnaissance. Language alone no longer gives away fraud. Your defense should therefore be based on clear processes, verification through a second channel, behavior-based detection, and regular training. The key takeaway is this: The best defense against AI-powered attacks is to handle AI better yourself than the attackers do.
FAQ
Can phishing emails still be recognized by spelling mistakes today?Not reliably. AI creates linguistically clean and context-specific messages, so you should instead pay attention to the occasion, sender, and processes.
How can I protect myself against voice cloning?For financially relevant requests, agree on a procedure in which you call the caller back on a number known to you. Also use code words.
Is a video call enough to confirm a person's identity?Not on its own. Deepfakes can be used in video calls. A small movement task or confirmation through another channel makes fraud more difficult.
Does signature detection help against AI-generated malware?It is not sufficient on its own because variants multiply quickly. Supplement it with behavior-based detection such as EDR with machine learning and zero-trust principles.

